[WEBINAR] Cyber Risk in the Mythos Era: Where Do We Begin?
6 October, 12pm - 1pm AEDT | 2pm - 3pm NZDT
Join cyber governance experts, Paul Hossack, Alex Ward, hosted by Angie Fung, as they explore the practical steps organisations can take to understand, assess, and manage cyber risk in the age of AI.
AI is changing the way business leaders view what's possible, but it's also creating an entirely new landscape of cyber risk, governance challenges, and regulatory expectations.
This new landscape has led to the Australian Signals Directorate retiring its existing Essential Eight framework, and the Five Eyes intelligence alliance declaring the speed at which frontier AI models are expected to transform cyber risk threats has exponentially increased from years to mere months.
In response, CIOs, CISOs, and business leaders are now asking, "Where do we begin?"
Join our cyber governance experts as they answer this question. They'll explore the practical steps organisations can take to understand, assess, and manage cyber risk in the age of AI.
By attending this webinar, you'll learn:
- Insights into emerging threats
- How to establish effective governance frameworks
- How to develop a roadmap for strengthening organisational resilience in an increasingly complex digital environment
This session will provide actionable guidance on AI governance, risk management, and regulatory considerations that are essential for building a secure foundation for advancing AI adoption.
Our Speakers
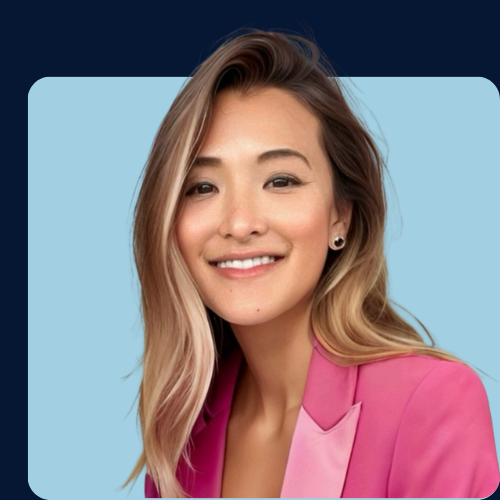
Angie Fung, General Manager - Strategy & Security Integration, VITG Group [HOST]
Angie Fung is a strategic leader with over 15 years of experience driving transformation and operational excellence across technology services. As General Manager, Strategy & Security Integration at VITG, she leads initiatives focused on business strategy, M&A integration, and organisational performance.
Angie has held senior leadership roles across cybersecurity, professional services, M&A integration, and business transformation at Telstra Purple, Telstra, and Ernst & Young.
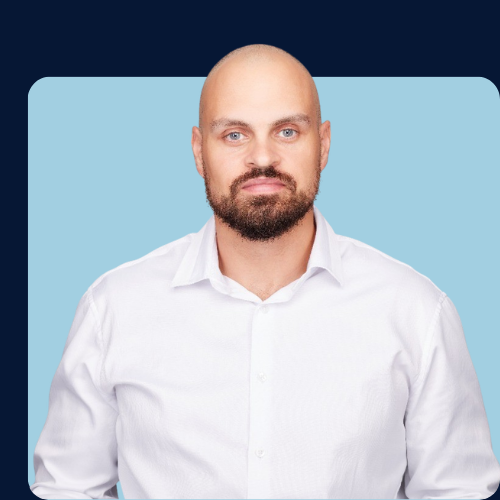
Paul Hossack, Principal GRC Consultant, Security Centric
Paul Hossack is a trusted cyber security advisor with experience across defence, government, banking, energy, and telecommunications. With expertise spanning IRAP, Essential Eight, ISO 27001, NIST, and APRA CPS 234, as well as being an endorsed IRAP Assessor and ISO 27001 Lead Auditor, he helps organisations navigate cyber and AI risk while balancing innovation, resilience, and compliance.
Known for his pragmatic, business-first approach, Paul cuts through complexity to help technology leaders make difficult decisions and turn security into a strategic business enabler.
Alex Ward, Head of GRC, Security Centric
Alex Ward is the Head of GRC and vCISO Services at Security Centric, with extensive experience helping organisations across Australia, New Zealand, and globally navigate cybersecurity, risk, and compliance requirements.
A certified PCI QSA and ISO 27001 Lead Auditor and Implementor, Alex specialises in aligning security outcomes with business objectives through practical, risk-based approaches. He works closely with organisations to address security challenges, improve cyber resilience, and build long-term security roadmaps that support sustainable growth.